
Every team is building agents. Someone has to set the rules.
Write the rules in one place, and every agent your teams build inherits them on day one. Nobody has to be asked twice, and nobody has to be trusted to remember.
UNIVERSAL GOVERNANCE CONTEXT
UNIVERSAL GOVERNANCE CONTEXT
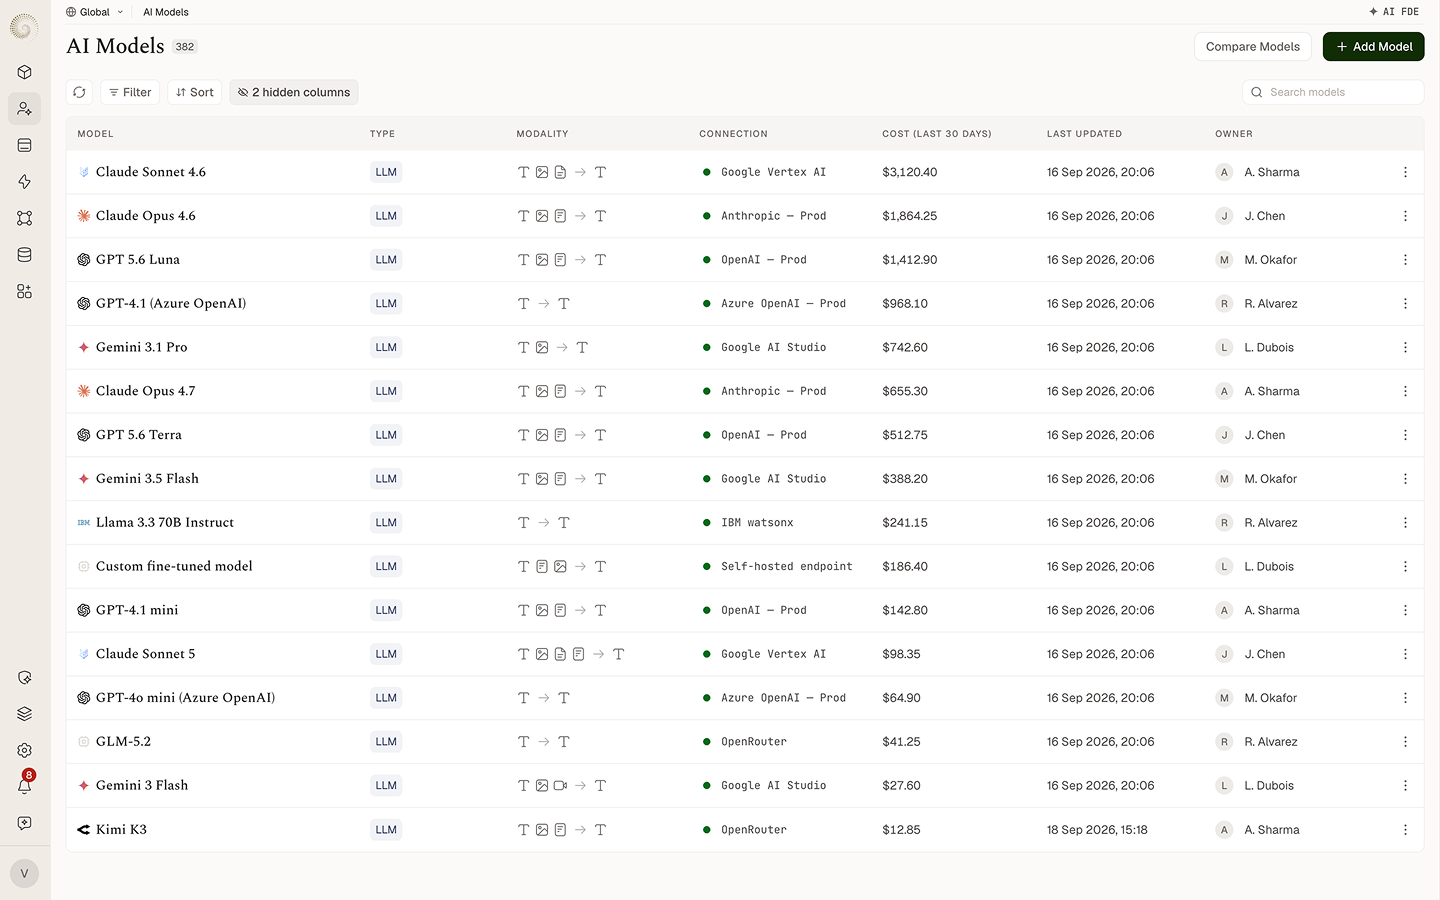
AI models — approved models from any provider live in one list, so you can see where each is used, what it costs, and swap or retire one without chasing every project.
AI models
The models you have approved, from any provider, kept in one list with what each one costs.
Compliance tools — the rules your risk and privacy teams already wrote are checked on every request and every action, before it runs.
Compliance tools
The rules your risk and privacy teams already wrote, applied to agents instead of rewritten for them.
Identity and access systems — an agent acts as the person or system it is working for, and can only reach what they could reach themselves.
Identity and access systems
Who each person is and what they are allowed to see. Agents inherit exactly that.
AI models — approved models from any provider live in one list, so you can see where each is used, what it costs, and swap or retire one without chasing every project.
Stop AI incidents before they cost you.
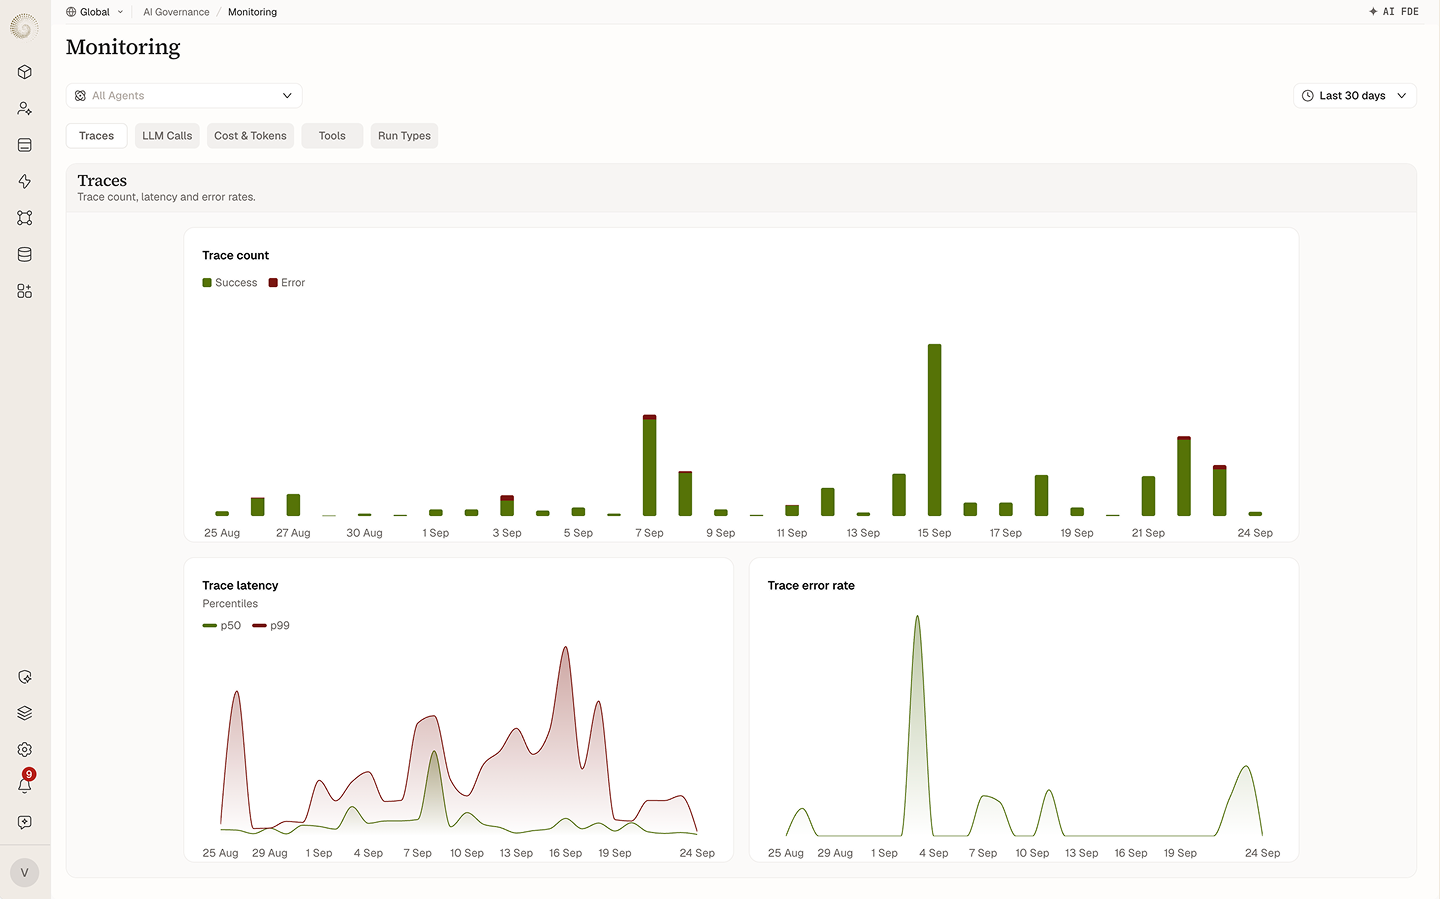
Set the rules, watch every agent in real time, and step in the moment something needs a person.
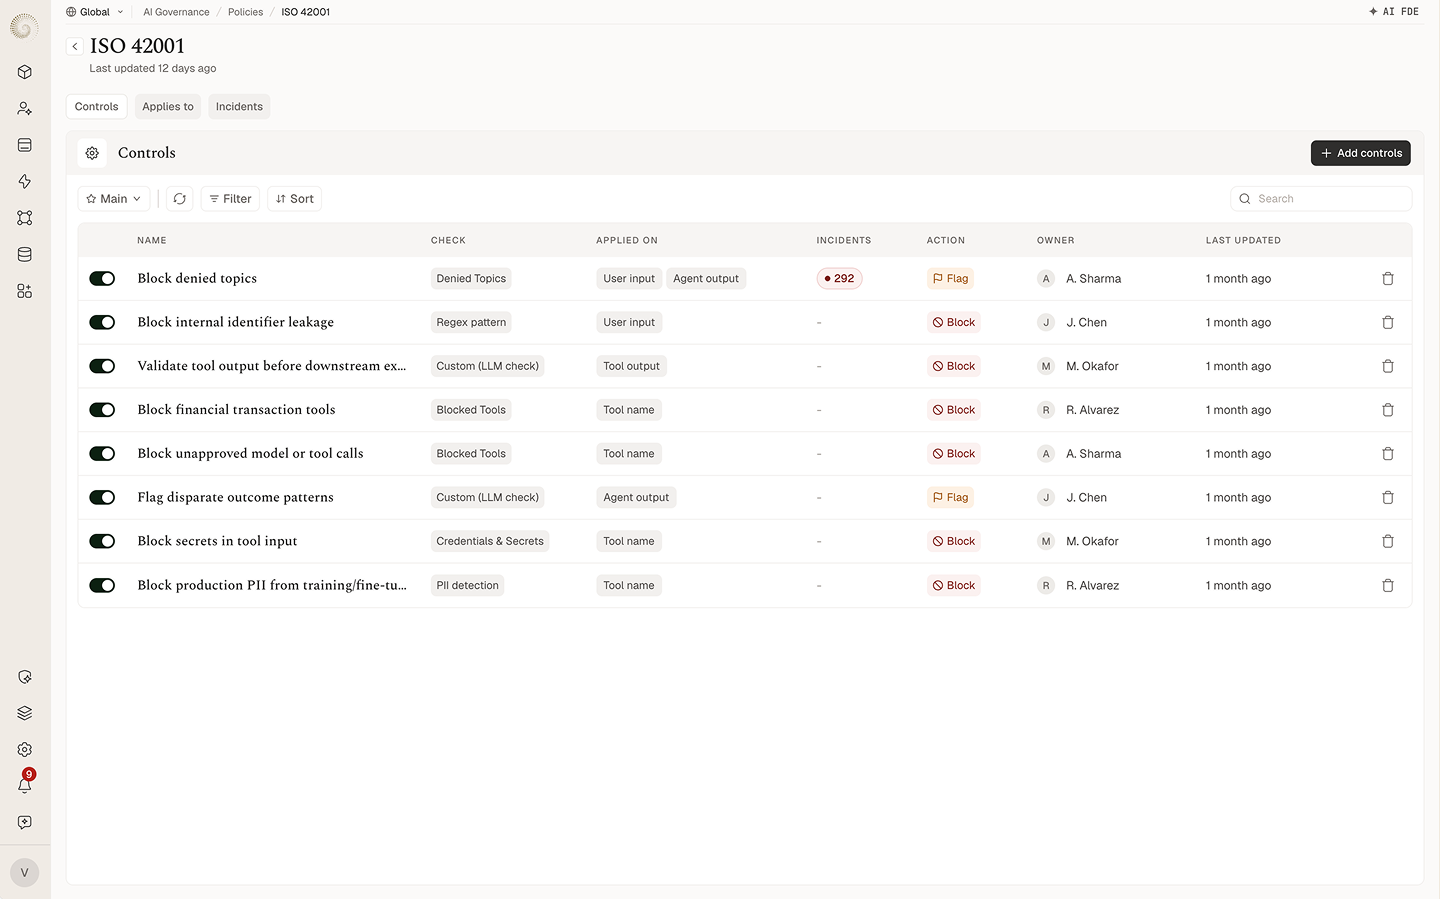
Write the rules once, in plain settings.
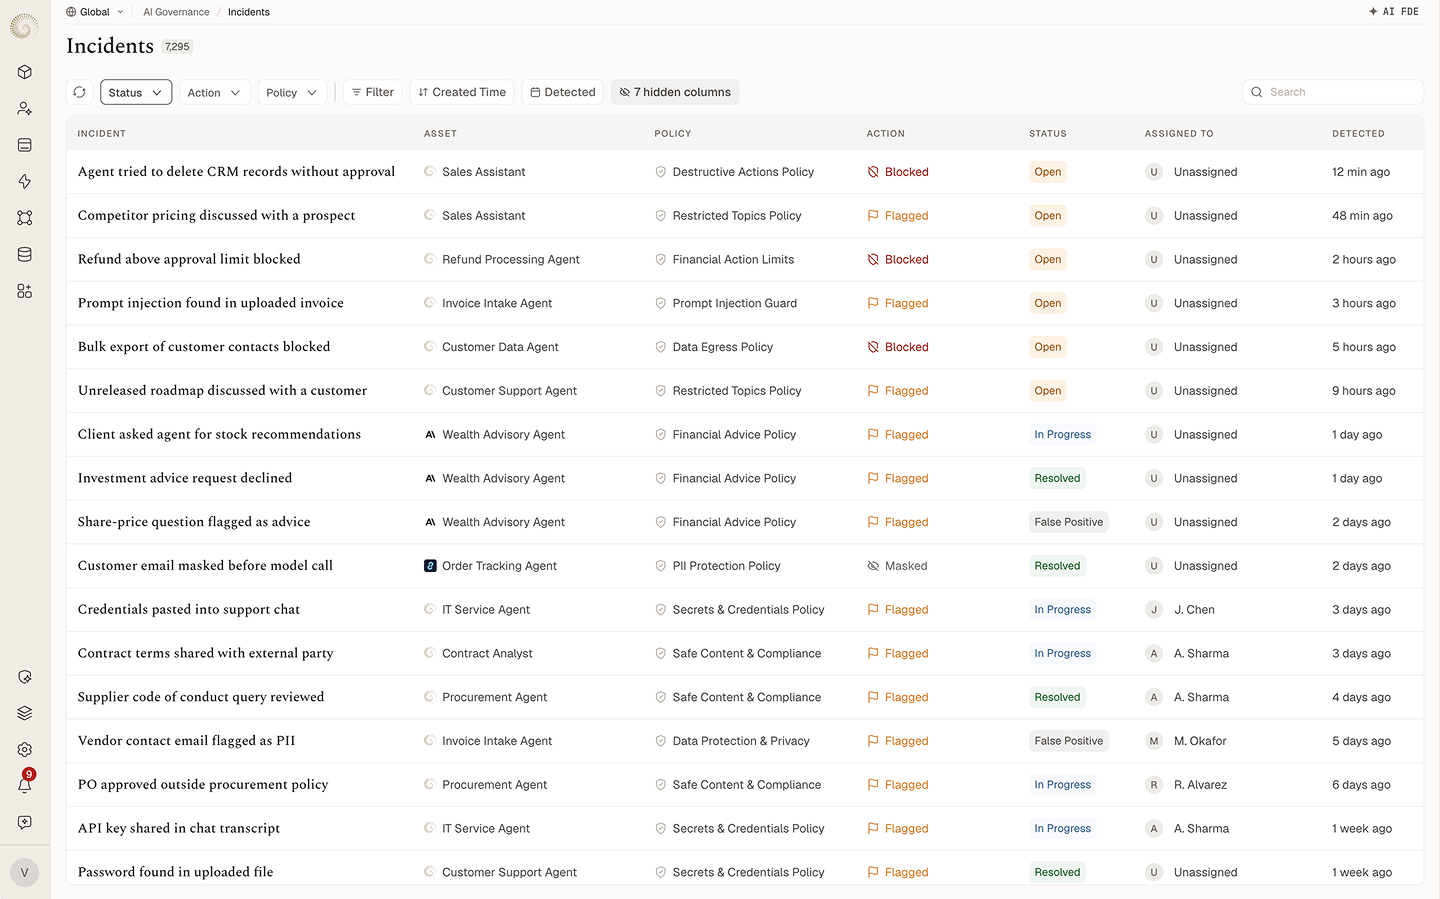
Check every request and every action before it runs.
Hide personal and financial data before a model sees it
Choose the topics agents must not discuss and the actions they must not take
Require a person to approve the actions you decide are too big to automate
01
Rules
01
Rules
Keep every AI action within the rules you set.
Follow one refund from request to approval. Sensitive data stays hidden, a person signs off on the amount that matters, and every step is recorded.

Asks the AI agent to refund order #4412 for a customer whose delivery never arrived.

Opens the order and the customer's delivery history. It cannot see anything the service agent isn't allowed to see.
Reads the case notes. The customer's card number is hidden before the AI ever sees it.

The refund is $640 — over the $500 limit your team set. The agent stops and asks. The manager approves in Slack.
Issues the refund and emails the customer. Who asked, what it saw, who approved and what it did are all written down.
Someone asks
A person or another system starts the request. Every request goes through the same path.
The agent gets only the access it needs
It works with the permissions of the person or system it is acting for. If they can't see a record, neither can the agent.
Your rules are applied
Your security team writes the rules once. UnifyApps checks every request and every action against them before they run, and hides sensitive data like card numbers.
A person approves what matters
You decide which actions need a human. Like a refund over a limit, a contract change, a payment. The agent waits for the answer.
Everything is recorded
Every step is kept: who asked, what the agent saw, who approved, what changed.
Set the governance layer once. Every agent your teams build works inside it.
Governance stops being work you redo and becomes an asset you reuse.

Know what every agent did Searchable records show each action, its reason, and who or what performed it.

Protect data everywhere it moves
Apply encryption and security controls automatically across every workflow.

Keep sensitive data private
Sensitive fields are masked inside the flow, before a model ever sees them.

SOC 2 and ISO certified
Independently audited against industry security and privacy standards.

GDPR handled
Residency, consent and subject rights managed at the platform layer.

Test changes before they go live
Review and evaluate updates before they reach production.
Security & Compliance
Industry-leading security and privacy standards.


