


Google People and Sharing covers Google Contacts and the Google Workspace directory: a user's own contacts, their "Other contacts" (people they have interacted with but not saved), and the people in their organization's directory. The UnifyApps Google People and Sharing connector uses the Google People API to create, update, delete, list and search contacts, copy other contacts into the user's contacts, search the directory, read the signed-in user's profile, and react to new or updated contacts from workflows and agents.
This guide covers every authentication type available on the connection form, and the actions and triggers supported, along with the Google scope each one needs.
Authentication
Before you begin, you should have the following information:
Connection name: a descriptive name such as MyAppGooglePeopleIntegration, so the connection is easy to identify later.
Authentication type: select the type of authentication for connecting to your Google account:
OAuth
OAuth with Client Credentials
Service Account
Every authentication type has an optional Scopes field. By default it selects all twelve scopes the connector offers: contacts, contacts.readonly, contacts.other.readonly, directory.readonly, user.addresses.read, user.birthday.read, user.emails.read, user.gender.read, user.organization.read, user.phonenumbers.read, userinfo.email and userinfo.profile, which together cover every action below. Choose narrower scopes only if you know which actions the connection will run; see the Scopes Required column in the tables below.
1. OAuth
Use this when you want to connect with your own Google account and do not need to create a Google Cloud app.
Enter a Connection name.
Select OAuth as the Authentication type.
Keep the default Scopes, or select the scopes you need.
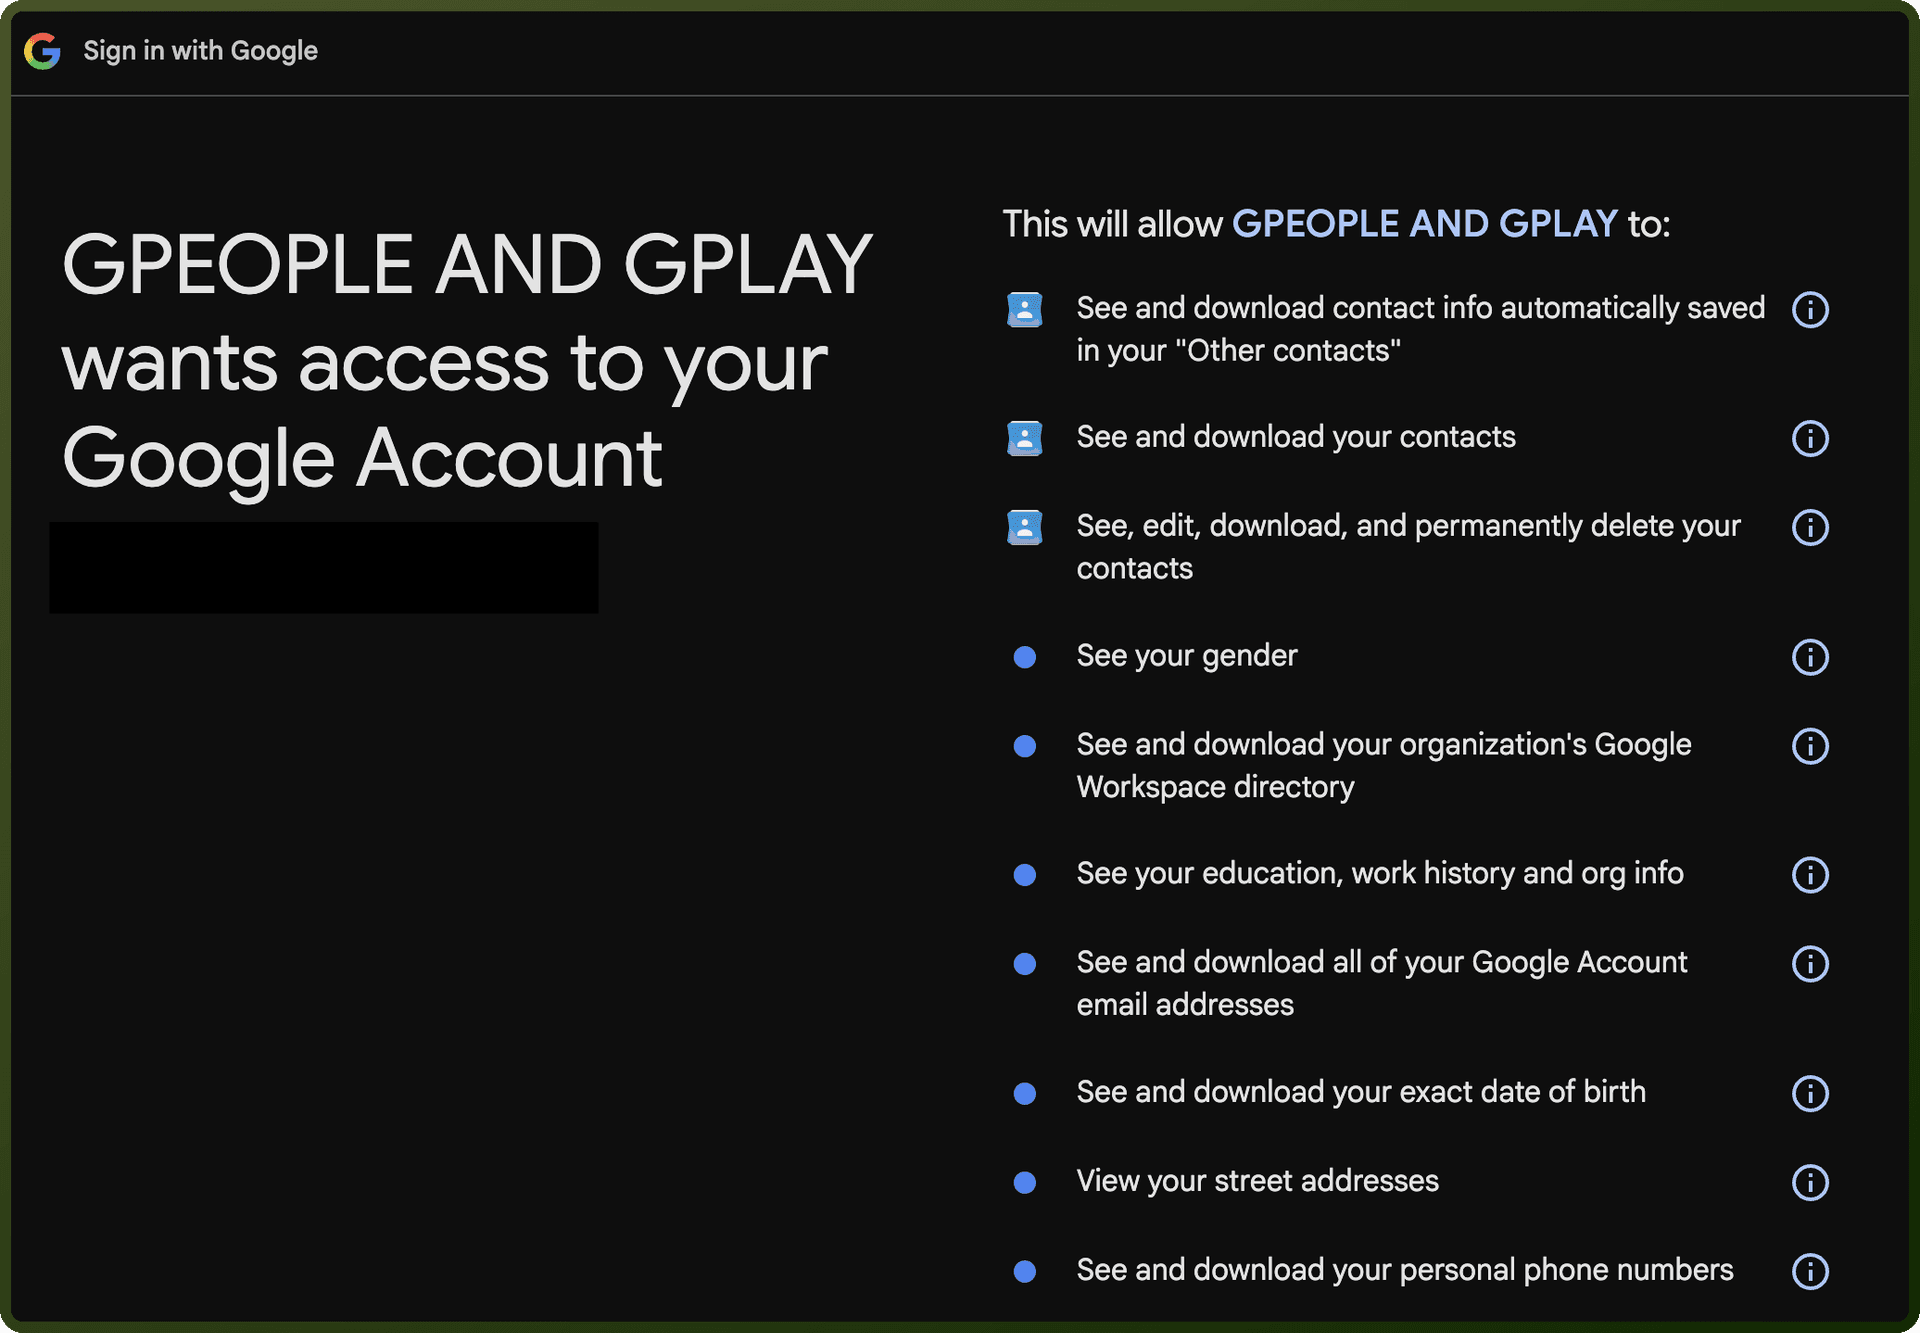
Click Authorize. You are redirected to the Google sign-in page.
Sign in with the Google account whose contacts the connection should use.
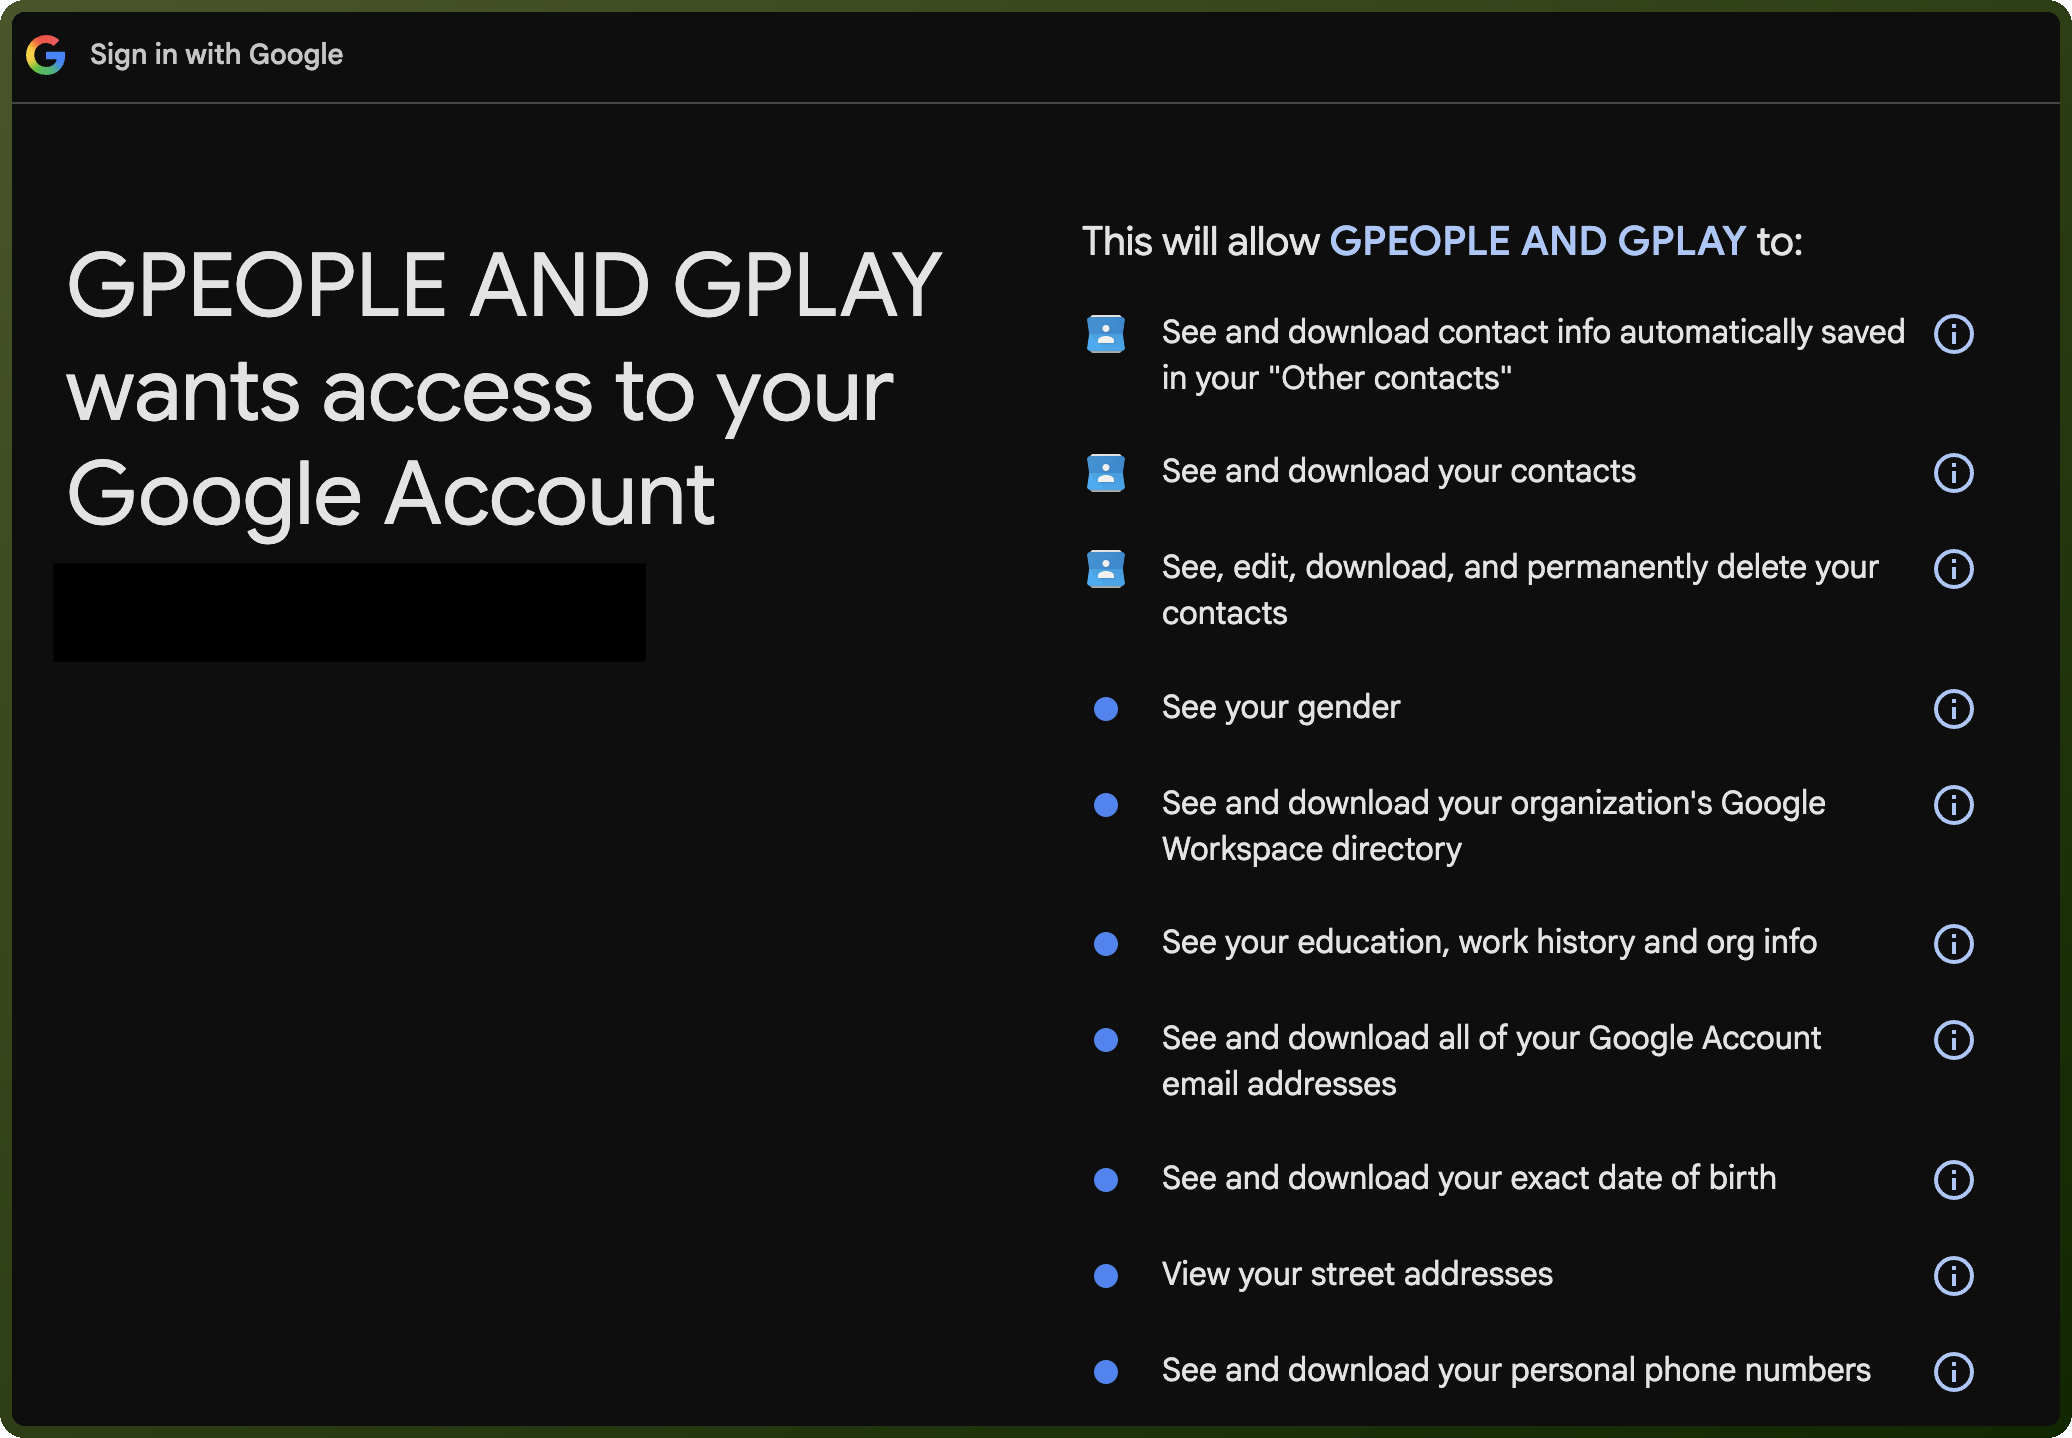
Review the permissions on the consent screen and click Allow.
You are redirected back to UnifyApps with a confirmation that the account is connected.
2. OAuth with Client Credentials
Use this when your organization wants the connection to use its own Google Cloud OAuth client, while actions still run as the Google user who signs in.
Step 1: Create an OAuth client in Google Cloud
In the Google Cloud Console, select or create a project, and enable the People API under APIs & Services → Library.
Go to Google Auth platform → Branding. If you see Google Auth platform not configured yet, click Get Started, enter an App name, User support email, Audience and contact email, and click Create.
Go to Data Access, click Add or Remove Scopes, select the People API scopes the connection will use, and click Save. If the audience is External, add the users who will sign in under Audience → Test users.
Go to Google Auth platform → Clients and click Create Client. Choose Web application as the Application type and enter a name.
Under Authorized redirect URIs, click Add URI and paste the Callback URL shown on the UnifyApps connection form (it is copyable and differs per environment).
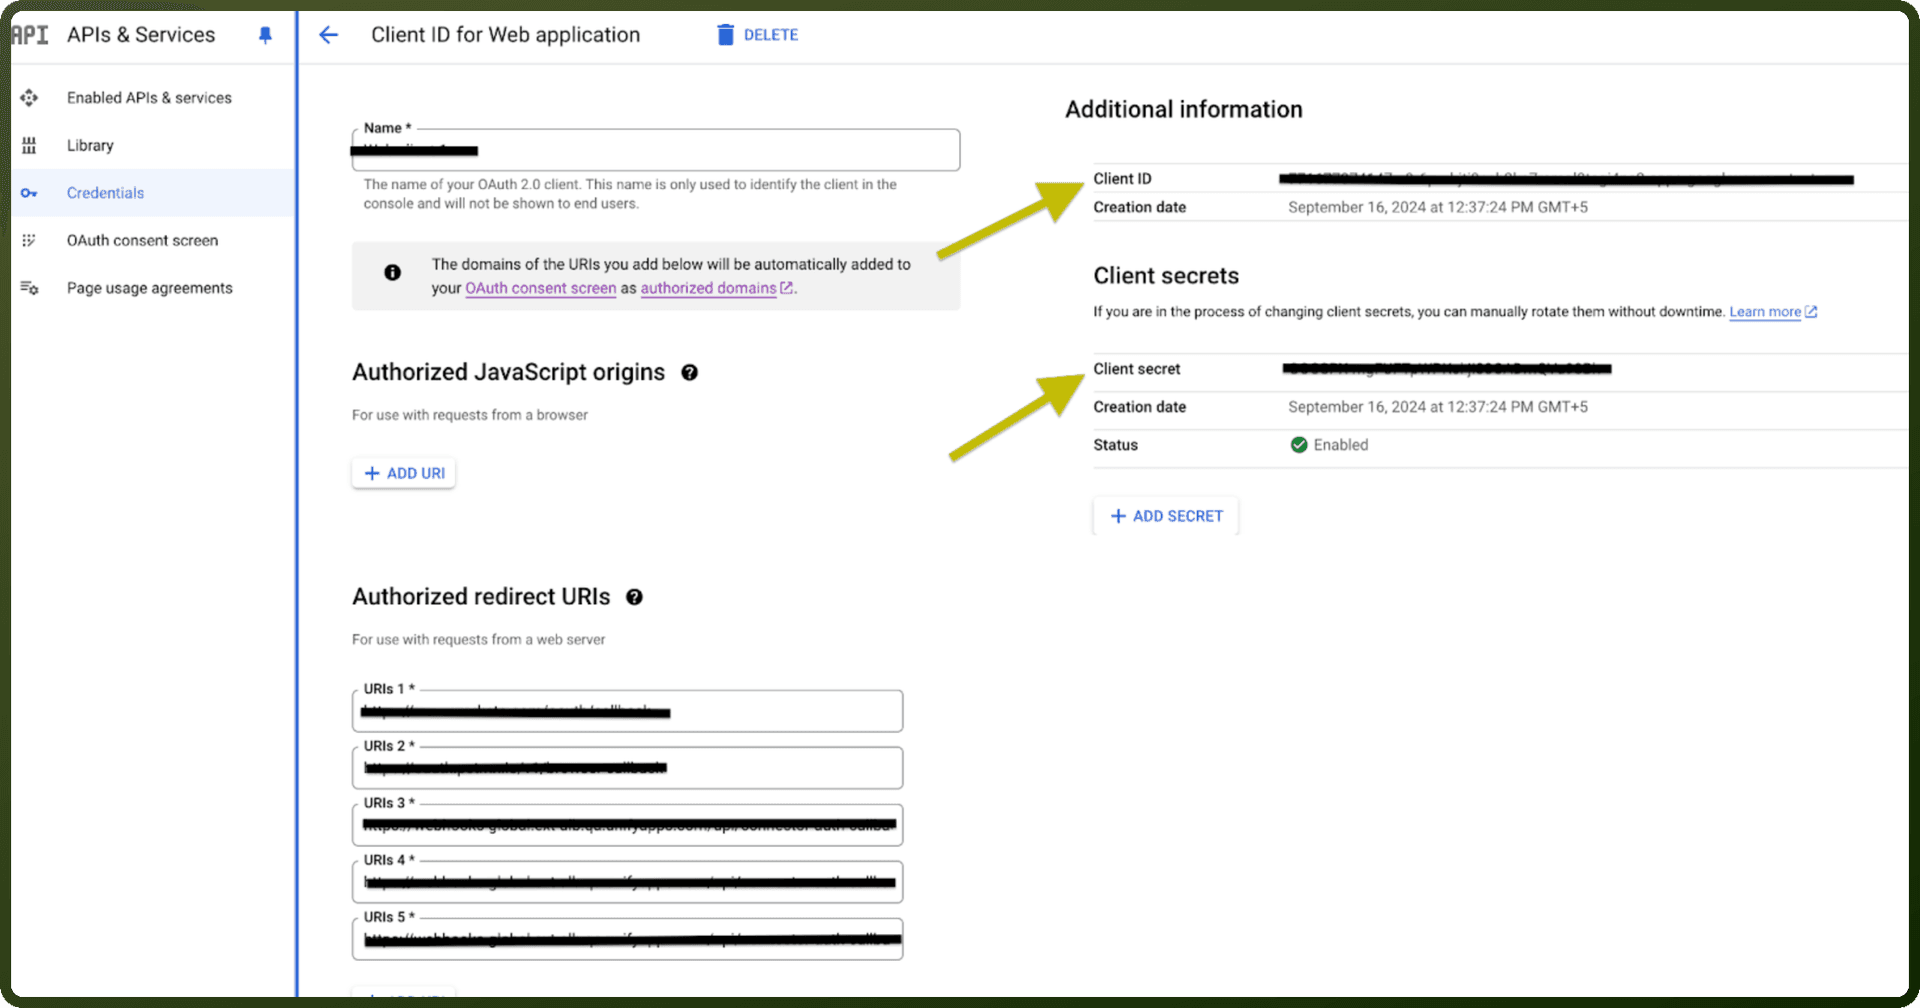
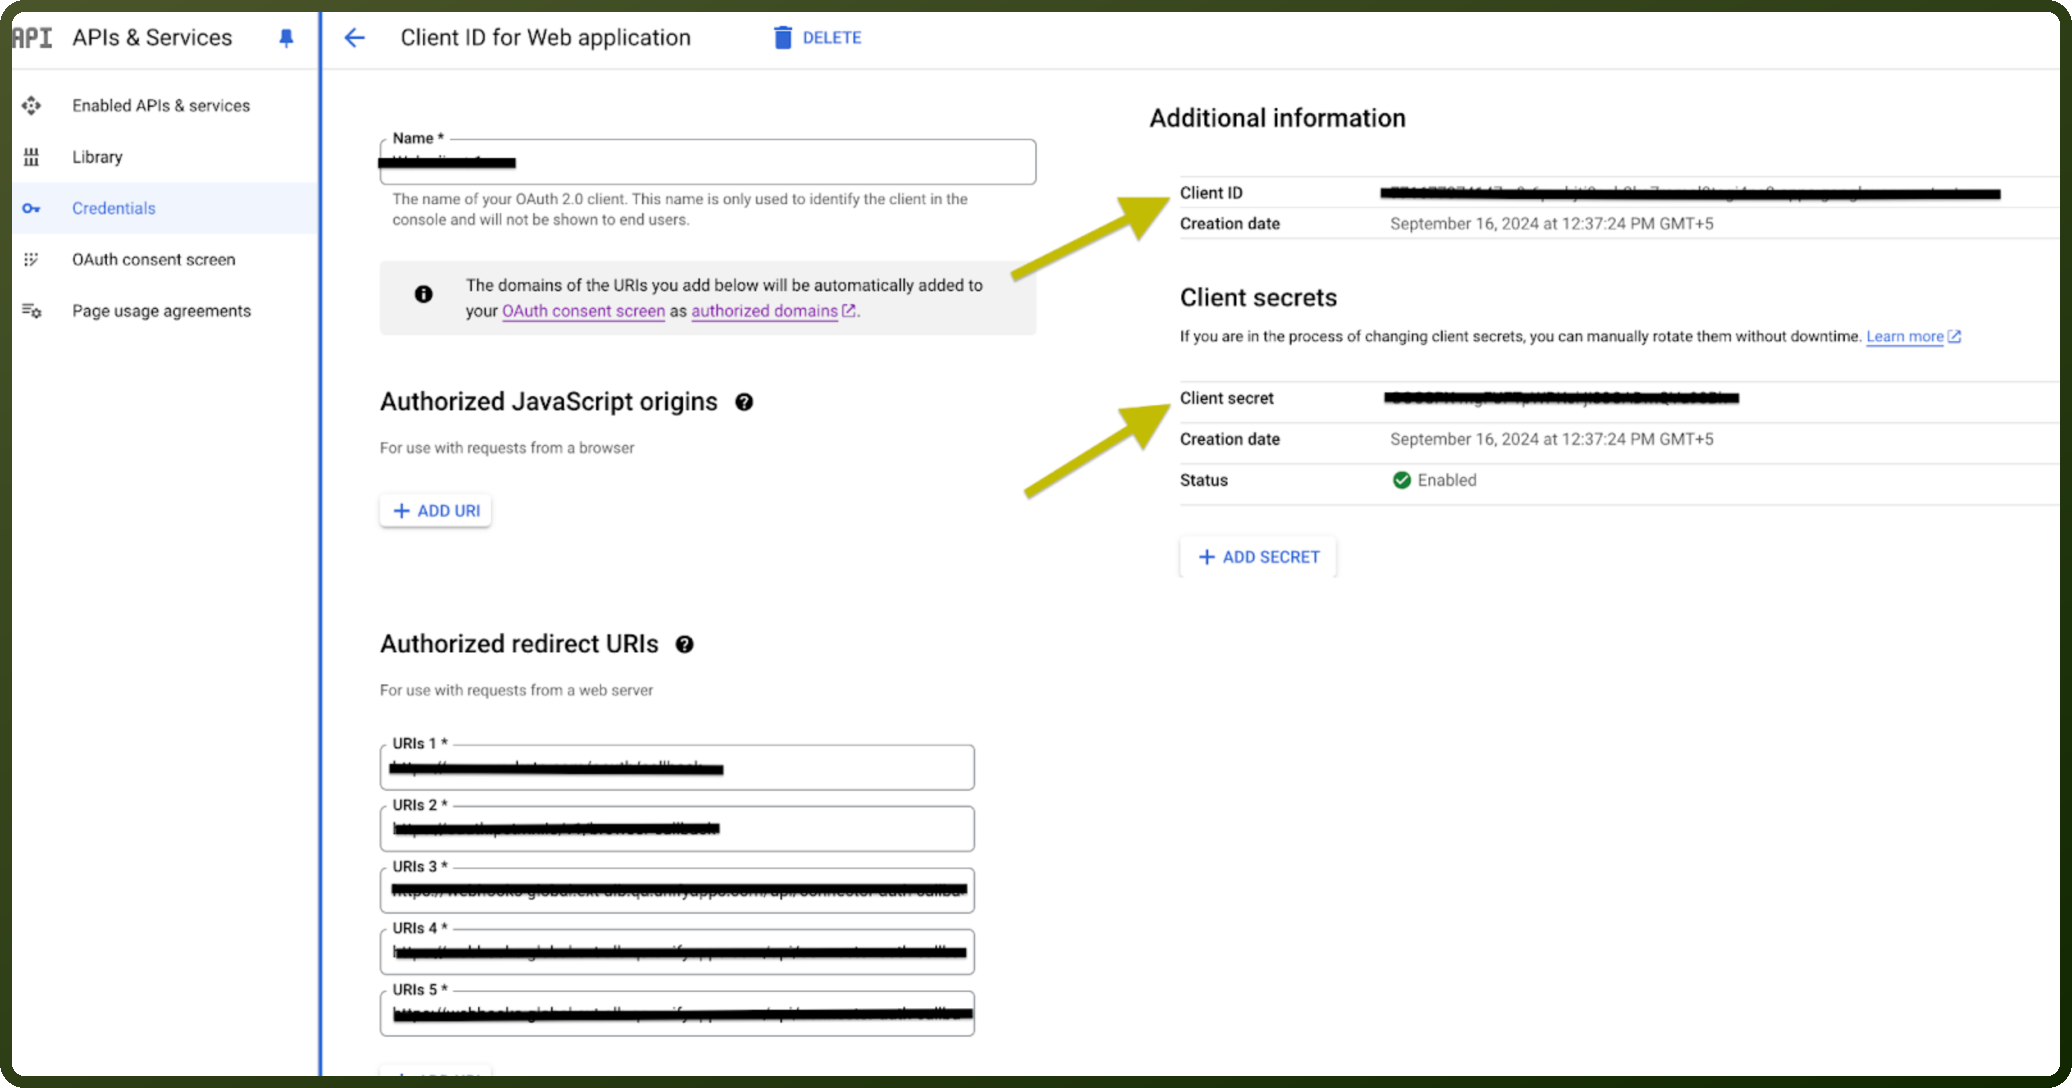
Click Create, then copy the Client ID and Client secret. Copy the secret immediately: Google shows it only once.
Step 2: Connection setup in UnifyApps
Open Connections → New Connection → Google People and Sharing and enter a Connection name.
Select OAuth with Client Credentials as the Authentication type.
Enter the Client ID and Client secret copied from Google Cloud.
Select the same Scopes you added to the consent screen.
Click Authorize, sign in with Google and click Allow on the consent screen.
Confirm the success message after the redirect back to UnifyApps.
3. Service Account
Use this for Google Workspace domains, where a service account acts on behalf of a user in the domain through domain-wide delegation. No user has to sign in.
Step 1: Create a service account in Google Cloud
In the Google Cloud Console, select or create a project, and enable the People API under APIs & Services → Library.
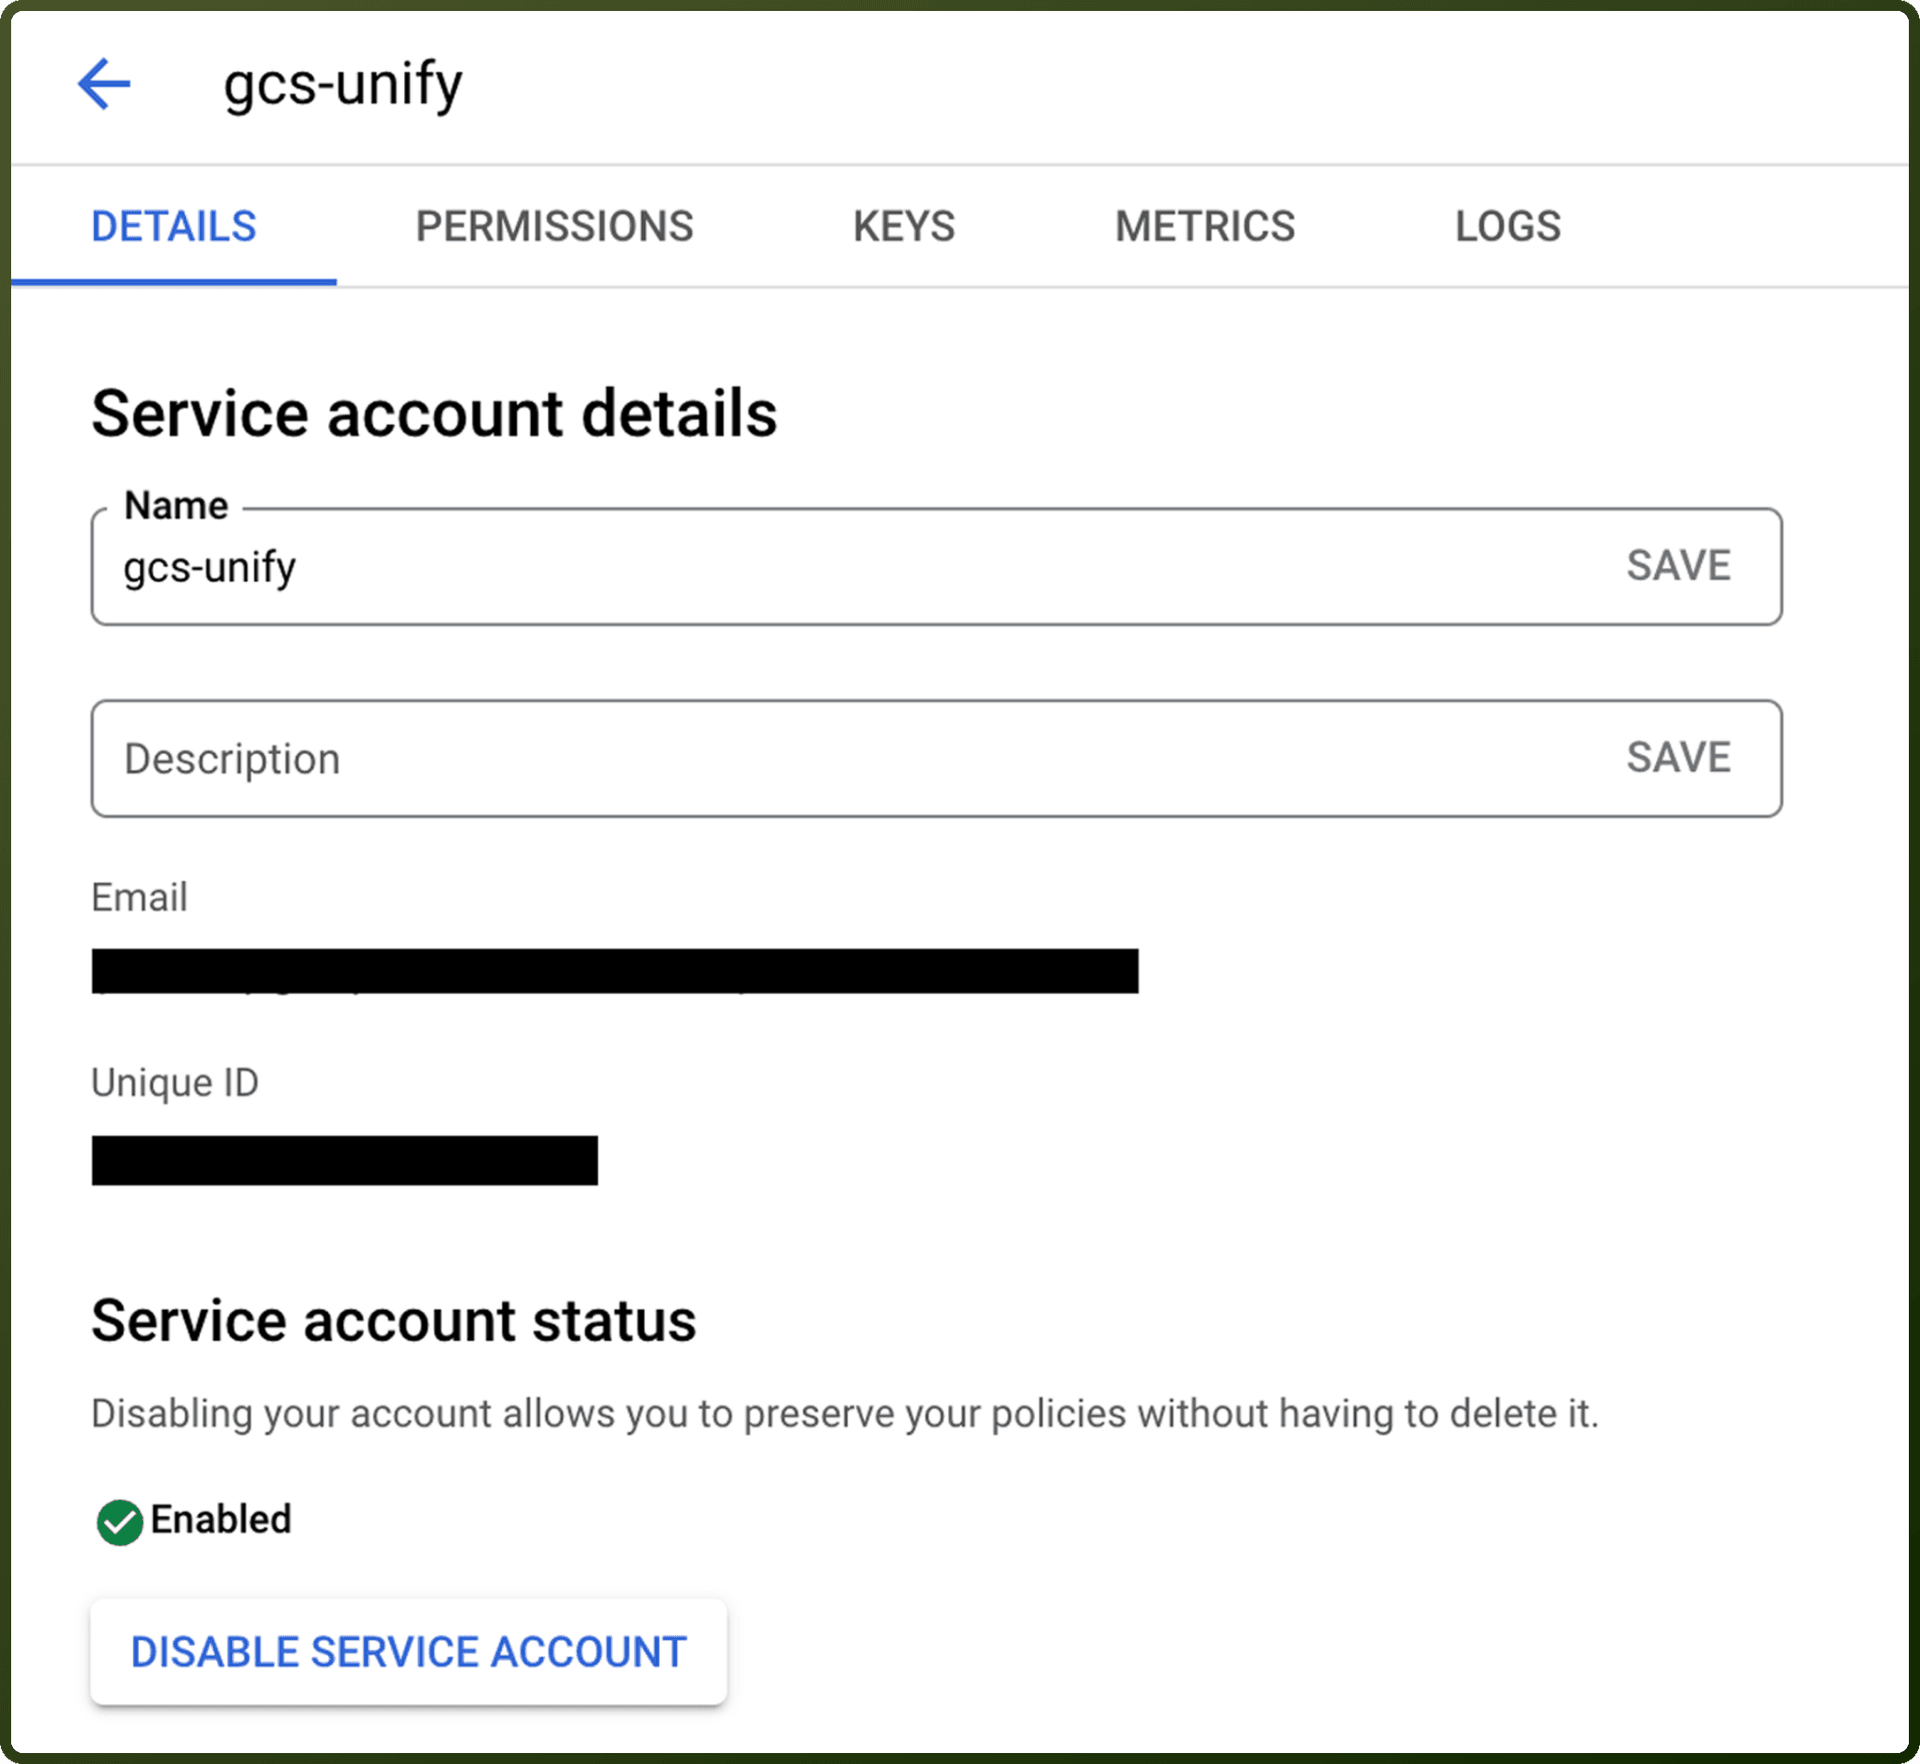
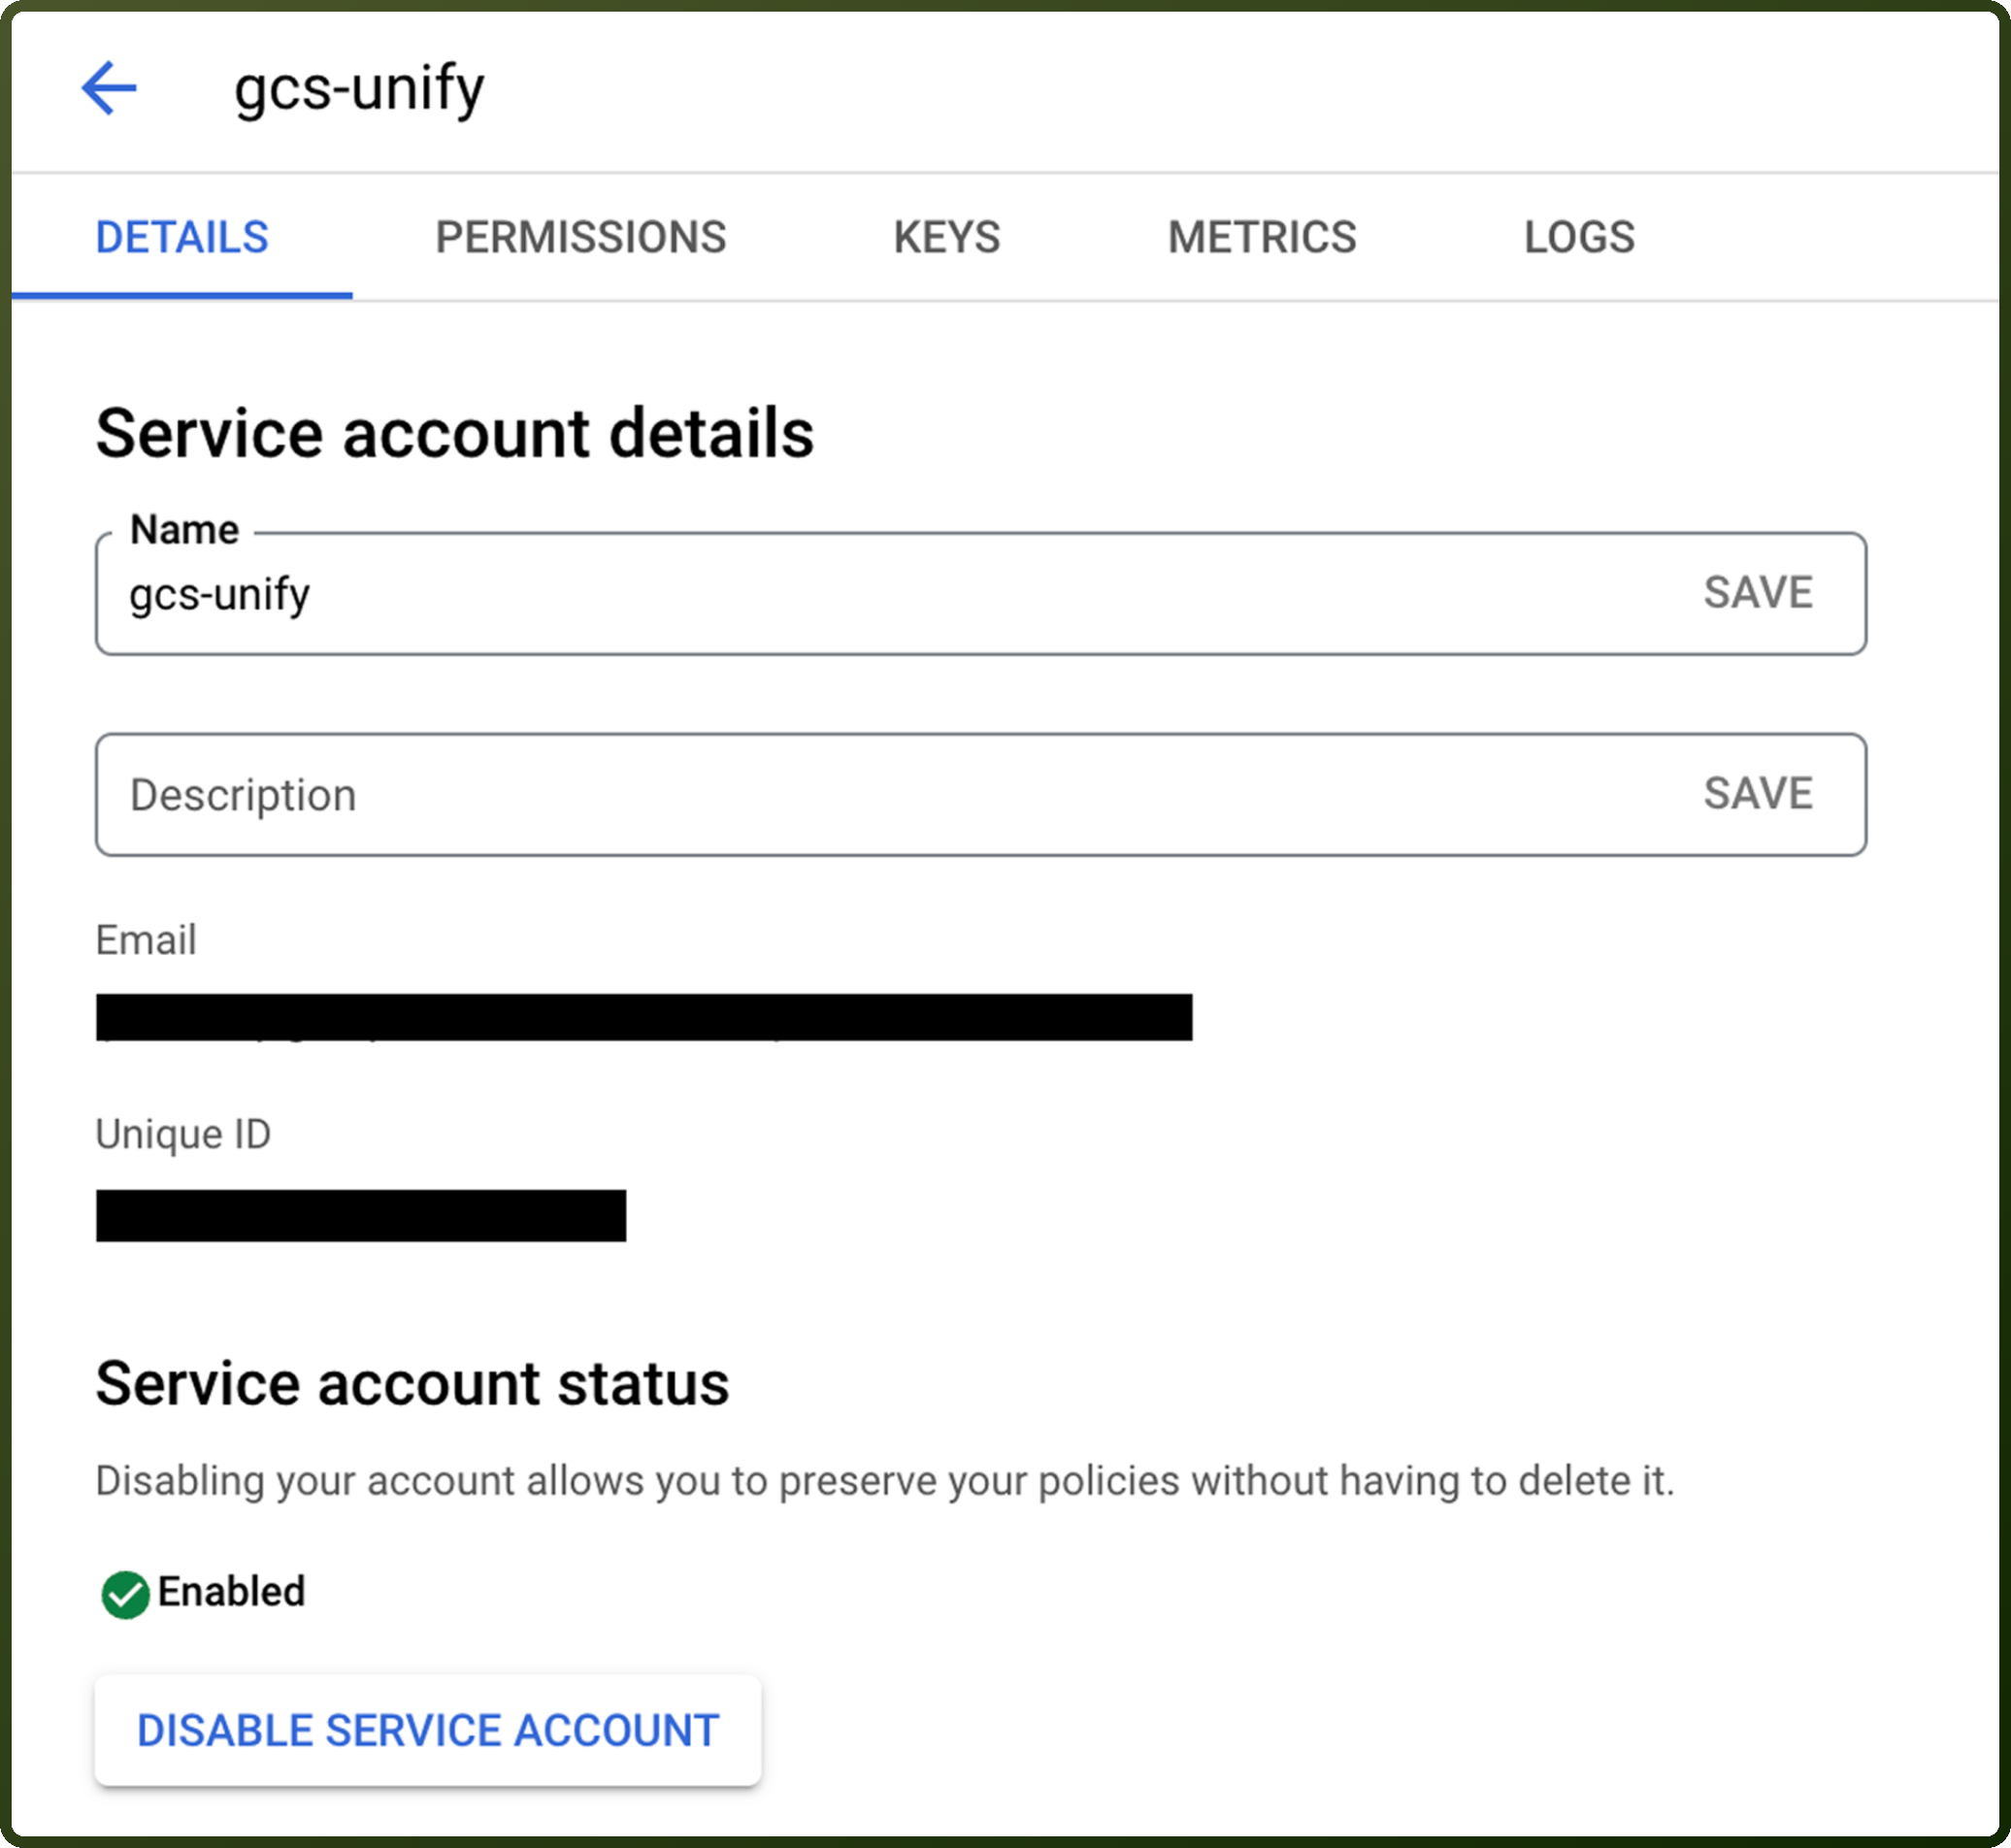
Go to IAM & Admin → Service Accounts and click Create service account. Enter a name and click Done.
Open the service account and copy its Email. Click Show advanced settings and, under Domain-wide delegation, copy the Client ID used in the next step.
Go to the Keys tab → Add key → Create new key, choose JSON and click Create. The downloaded file holds the
client_emailandprivate_key. Store it securely.
Step 2: Give the service account domain-wide access
A Google Workspace super administrator opens the Admin console → Security → Access and data control → API controls.
Click Manage Domain Wide Delegation → Add new.
Enter the service account's client ID, add the OAuth scopes the connection will use (for example
https://www.googleapis.com/auth/contacts), separated by commas, and click Authorize. See Delegate domain-wide authority to your service account for details.
Note: every scope selected in the UnifyApps Scopes field must also be authorized here, or Google refuses to issue a token. If you keep the default scopes, authorize all twelve. Google says changes can take up to 24 hours to apply.
Step 3: Create the connection in UnifyApps
Select Service Account as the Authentication type.
Enter the GCP Project Service Account Email and paste the Private key from the JSON key file.
Enter the User email of the Workspace user whose contacts the connection acts on.
Select the Scopes granted in Step 2.
Click Create. This connector has no connection test, so the credentials are first checked when an action runs.
Actions
Scopes are shown in short form: contacts means https://www.googleapis.com/auth/contacts. Any broader scope also works; contacts covers every action except Search directory people and Get current authenticated user.
Actions | Description | Scopes Required |
|---|---|---|
| Copies an "Other contact" to the user's contacts in Google People and Sharing. | contacts.other.readonly (or contacts) |
| Creates a contact in Google People and Sharing. | contacts |
| Deletes a contact in Google People and Sharing. | contacts |
| Lists all contacts in Google People and Sharing. | contacts.readonly (or contacts) |
| Gets the profile of the signed-in user in Google People and Sharing. | userinfo.profile; plus user.emails.read, user.addresses.read, user.birthday.read and user.phonenumbers.read to include those fields |
| Lists the "Other contacts" in Google People and Sharing. | contacts.other.readonly |
| Searches for contacts that match the specified query in Google People and Sharing. | contacts.readonly (or contacts) |
| Searches the Google Workspace directory for people that match the specified query. | directory.readonly |
| Searches for "Other contacts" that match the specified query in Google People and Sharing. | contacts.other.readonly |
| Updates a contact in Google People and Sharing. | contacts |
Triggers
Triggers | Description | Scopes Required |
|---|---|---|
| Triggers when a new contact is created in Google People and Sharing. | contacts.readonly (or contacts) |
| Triggers when a contact is created or updated in Google People and Sharing. | contacts.readonly (or contacts) |